Once your practice is captured under Tranche 2, six obligations apply immediately: enrol with AUSTRAC, appoint a named AML/CTF compliance officer, complete a business-wide ML/TF risk assessment, build AML/CTF policies from it, run customer due diligence before providing any designated service, and keep records for the legally required minimum period, generally several years. There’s no grace period once you’re in scope. Enrolment and a working risk assessment come first, before you touch a single client file for a designated service.
TL;DR:
- Enrolment with AUSTRAC is mandatory for practices providing designated services under Tranche 2, and must be completed before onboarding any clients or providing services.
- Risk assessments must cover money laundering, terrorism financing, and proliferation financing risks, and policies must be created from these assessments with reviews every three years or upon significant practice changes.
- Customer due diligence must be done before service delivery, verifying identities and beneficial ownership for individuals, companies, and trusts, with ongoing re-screening essential for high-risk clients.
- Suspicious matter reports must be filed within 24 hours for terrorism-related suspicions and three business days for others, with cash transactions of $10,000 or more requiring immediate reporting.
- Practitioners must retain AML/CTF records for at least seven years, ideally eight, and implement training for all relevant staff, with documented processes to demonstrate ongoing compliance.
Table of Contents
- What are the enrolment obligations for accountants under AML/CTF?
- What must the risk assessment and AML/CTF policies cover?
- What customer due diligence steps are required before onboarding a client?
- How and when must accountants report suspicious matters?
- How long must accountants keep AML/CTF records, and how should training work?
- What should accountants do in the next 30 to 90 days?
- What does customer due diligence look like in practice for accountants?
- What should you do the day AUSTRAC notifies you of in-scope status?
- What happens if an accounting practice fails to comply with AML/CTF obligations?
- How an integrated platform supports these obligations
- How AML Guard supports accounting practices meeting AML/CTF obligations
- Sources
- FAQ
What are the enrolment obligations for accountants under AML/CTF?
Enrolment is the step most newly captured practices miss, largely because it feels like paperwork rather than compliance. It isn’t optional and it isn’t automatic: no one enrols you.
For many practices, enrolment windows opened on 31 March 2026, with obligations applying from 1 July 2026 for firms providing captured services. If your practice offers any of the professional services brought into scope under the Tranche 2 reforms, you need to check your enrolment status now, not when a client engagement forces the question.
Whether a specific service you provide is a designated service depends on the circumstances of the engagement, not just your job title. That distinction matters enough that it deserves its own explanation, which is why AML Guard covers it separately.
Practical steps for enrolment:
- Register through AUSTRAC Online, using the practice’s ABN and details of the principal or nominated compliance officer.
- Nominate a named AML/CTF compliance officer at the point of enrolment, not afterwards.
- Keep enrolment details current: changes to ownership, address, or the compliance officer must be updated promptly.
- Check pre-commencement customer rules before assuming existing clients are exempt. Practices frequently misread this exception: CDD can still be triggered where a client’s risk profile changes or they request a new designated service after commencement.
If you’re unsure when your obligations actually started, When Does AML Compliance Actually Start? walks through the pre-commencement distinction in more depth.
What must the risk assessment and AML/CTF policies cover?
A business-wide ML/TF risk assessment isn’t a formality you complete once and file away. Under section 26C of the AML/CTF Act, it must assess money laundering risk, terrorism financing risk, and proliferation financing risk, a category many practices overlook because it sounds like it belongs to defence exporters, not accountants. It doesn’t. Proliferation financing covers the movement of funds tied to weapons programs, and every reporting entity’s risk assessment must address it regardless of client base.
Your policies then need to be built from that same risk assessment, not drafted separately and hoped into alignment. A supervisor reviewing your program checks for exactly this consistency: if your policies describe controls that don’t match the risks your assessment identified, that gap is the first thing an audit will flag.
- Identify and document your ML/TF/PF risk exposure across clients, services, delivery channels, and geography.
- Translate each identified risk into a specific control in your AML/CTF policies.
- Review the risk assessment at least once every three years, or sooner if your service mix changes materially.
- Arrange an independent evaluation at least every three years, separate from your internal review cycle.
Pro Tip: Don’t wait for the three-year mark to review your risk assessment if you add a new service line, take on overseas clients, or start handling significant cash transactions. A material change in your practice is a trigger in its own right, not just a calendar event.
What customer due diligence steps are required before onboarding a client?
Initial CDD has to be completed before you provide a designated service, not during it and certainly not after. The only exception sits within the narrow pre-commencement customer rules, and even those don’t hold once a client’s circumstances change.
For individuals, that means verifying identity against reliable, independent documentation before the engagement proceeds. For companies, beneficial ownership resolves against the company’s ACN. Trusts and self-managed super funds work differently: you reach the beneficial owner through the trust’s corporate trustee, which runs its own determination on its own ACN, with the trust deed itself requiring officer review rather than automated resolution.
Core CDD steps for accountants:
- Verify the client’s identity (individual, company, trust, or other structure) before providing the designated service.
- Resolve beneficial ownership for companies via ACN lookup.
- For trusts and SMSFs, identify the corporate trustee, resolve its ACN, and have an officer review the deed.
- Apply enhanced CDD where a client presents higher risk: complex ownership structures, politically exposed persons, cash-intensive businesses, or jurisdictions with weak AML controls.
- Re-screen clients on an ongoing basis, not just at onboarding, since sanctions and PEP status change over time.
Enhanced due diligence isn’t reserved for obviously suspicious clients. A strong majority of AML failures trace back to inadequate ongoing monitoring rather than a bad decision at onboarding. Ownership structures shift, directors change, and a client who looked low risk two years ago may not be low risk today.
How and when must accountants report suspicious matters?
Reporting obligations run on strict clocks, and missing them is a compliance failure in its own right, separate from whatever underlying conduct triggered the report.
- Suspicious matter reports (SMRs): submit within 24 hours if the suspicion relates to terrorism financing, and within three business days for other suspicious matters, under section 41 of the Act.
- Threshold transaction reports (TTRs): any physical cash transaction of $10,000 or more triggers a reporting obligation, regardless of whether anything about the client looks unusual.
- Annual compliance reporting: reporting entities must be able to demonstrate compliance through internal records, and AUSTRAC expects an annual compliance report reflecting the state of your program.
A suspicious matter doesn’t require certainty of wrongdoing. It requires reasonable grounds to suspect, which is a lower bar than most accountants assume when they first read the Act. If something about a transaction or client relationship doesn’t sit right and you can’t explain it satisfactorily, that’s usually enough to trigger the reporting clock.
How long must accountants keep AML/CTF records, and how should training work?
The legal minimum is seven years: records must be kept for seven years after they stop being relevant to your AML/CTF obligations, not seven years from the date they were created. That distinction affects long-running client relationships where the retention clock keeps resetting.
A tamper-evident audit trail (one that shows if a record has been altered after the fact, rather than merely claiming it can’t be) gives you more than the legal floor. Some platforms retain records for eight years, above the statutory seven-year minimum, specifically because supervisory reviews sometimes reach back further than the bare legal requirement.
- Every staff member who deals with clients or transactions needs AML/CTF training, not just the compliance officer.
- Multilingual training options matter in practices serving clients across diverse communities.
- Keep training completion records as part of your program evidence, since “we trained staff” without documentation carries little weight in a supervisory review.
Pro Tip: Treat your audit trail as evidence you’re building for a future version of yourself, not paperwork for today. The accountant who has to reconstruct a decision from three years ago with no record trail is the one who struggles most in an AUSTRAC review.
What should accountants do in the next 30 to 90 days?
Progress here is measured in documented actions, not intentions. A supervisor wants to see dates, owners, and evidence, not a verbal assurance that “we’re working on it.”
- Weeks 1 to 2: Confirm enrolment status on AUSTRAC Online; enrol if you haven’t already.
- Weeks 2 to 4: Appoint and document a named AML/CTF compliance officer, even if that’s you as sole practitioner.
- Weeks 3 to 6: Complete the business-wide ML/TF risk assessment, covering money laundering, terrorism financing, and proliferation financing.
- Weeks 5 to 8: Draft and approve AML/CTF policies derived from that risk assessment.
- Weeks 6 to 10: Stand up CDD workflows for new and existing clients, including beneficial ownership checks.
- Weeks 8 to 12: Commence staff training and start the seven-year record-keeping regime.
Smaller practices can use the accounting program starter kit as a base template, though larger or higher-risk firms will need to expand well beyond its scope.
What does customer due diligence look like in practice for accountants?
Generic CDD guidance rarely maps cleanly onto how accountants actually engage clients. A tax return client and a trust structuring client present very different verification paths.
For an individual tax client, CDD is comparatively simple: verify identity against a driver’s licence or passport, confirm residential address, and screen against sanctions and PEP lists before the engagement starts. Most practices already collect this information; the gap is usually in the screening step, which needs to happen before service delivery, not buried in an onboarding form nobody checks against a watchlist.
For a company client, the picture gets more layered. You verify the company’s registration and ACN, then resolve beneficial ownership against that ACN to identify individuals with effective control, typically anyone holding 25% or more, though risk-based judgement can lower that threshold for higher-risk structures. Directors and significant shareholders each need identity verification in their own right.
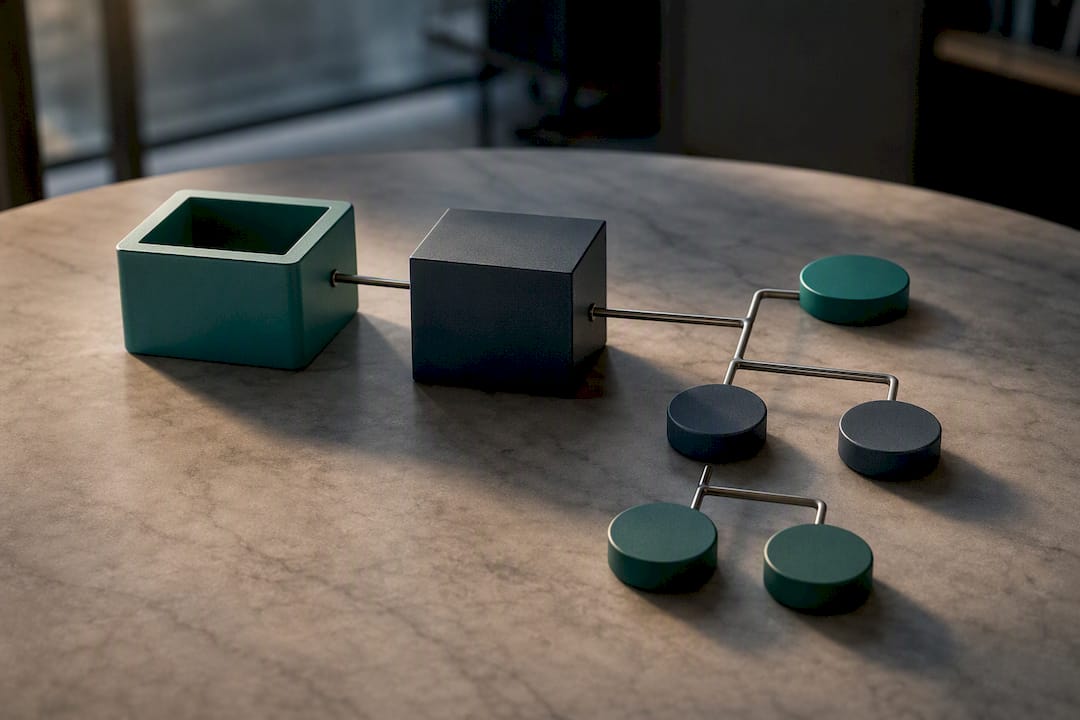
Trust and SMSF clients are where most errors happen. You don’t run beneficial ownership determination directly against the trust. Instead, you identify the corporate trustee, resolve beneficial ownership against that trustee’s own ACN, and have an officer review the trust deed to confirm beneficiaries, appointors, and control provisions. Treating a trust and its corporate trustee as interchangeable for CDD purposes is one of the most common technical mistakes accounting practices make.
For a cash-heavy retail client seeking advisory or bookkeeping services, enhanced due diligence usually applies from the outset: source-of-funds questions, more frequent re-screening, and closer scrutiny of transaction patterns become standard practice rather than an exception triggered later.
What should you do the day AUSTRAC notifies you of in-scope status?
An AUSTRAC notice confirming your practice is in scope isn’t a warning to eventually act on. It’s a trigger for a defined sequence of steps, and the clock on some of them starts immediately.
First, confirm or complete enrolment on AUSTRAC Online if you haven’t already, since notification of in-scope status assumes you’ll formalise your registration promptly. Second, formally appoint your AML/CTF compliance officer in writing, even where that person is the sole practitioner themself; the appointment needs to be documented, not just understood internally.
Third, pause any new engagements that would constitute a designated service until you have at least a baseline CDD process in place. This doesn’t mean halting your practice; it means not onboarding a new company or trust client for a captured service until you can verify identity and beneficial ownership properly.
Fourth, begin the business-wide risk assessment immediately rather than treating it as a document to get to eventually. AUSTRAC’s expectation is that a risk assessment exists and is actively used to shape your policies, not that it’s perfect on day one. A reasonable, documented assessment beats a delayed, comprehensive one every time a supervisor asks to see your program.
Fifth, communicate internally. Staff who deal with clients need to understand, even at a basic level, that new verification steps apply before they process new client instructions for a captured service. A notification that never reaches the people doing client-facing work achieves nothing.
What happens if an accounting practice fails to comply with AML/CTF obligations?
Non-compliance under the AML/CTF Act carries penalties, and AUSTRAC has both civil and criminal enforcement pathways available depending on the seriousness and intent behind a breach. Failing to enrol, failing to lodge required reports, or failing to maintain a program at all sit at the more serious end of that spectrum.
The practical risk for most practices isn’t a single dramatic incident. It’s a supervisory review that finds a risk assessment that doesn’t match your policies, a CDD process with no documented evidence, or a missing SMR that should have been lodged within the statutory window. Each of those findings compounds: a regulator that finds one gap tends to look harder for others.
If you discover a compliance gap yourself, before AUSTRAC finds it, document the gap, the remediation steps, and the timeline for fixing it. Self-identified and self-remediated gaps are treated very differently to gaps a regulator has to surface through its own review. Accountants sometimes assume that professional privilege shields client information from these obligations; it doesn’t. Legal professional privilege belongs to lawyers, not accountants, and even where it applies to legal advice, it doesn’t displace CDD or reporting duties under the AML/CTF Act.
The practical response to a compliance gap is the same regardless of size: fix the process, document what changed, and be ready to show a supervisor the before-and-after.
How an integrated platform supports these obligations
An accountant’s compliance burden multiplies fast once you’re tracking risk assessments, CDD, and reporting across separate spreadsheets and templates. Some platforms produce the risk assessment, AML/CTF policies, compliance action plan, and training manual as one linked set, so a change to your risk profile flows through to policies automatically rather than leaving them silently out of sync.
CDD runs end to end, with beneficial ownership resolved against a company’s ACN and multilingual staff training tracked with completion records. An officer still approves each determination before CDD proceeds: the platform automates the lookups and the record keeping, not the judgement calls that remain yours to make.
How AML Guard supports accounting practices meeting AML/CTF obligations
Some compliance platforms offer an alternative to piecing together spreadsheets, templates, and a compliance officer’s memory to meet Tranche 2 obligations. They provide accounting practices linked program artefacts (risk assessment, policies, compliance action plan, and training manual) that stay consistent because they’re generated from the same answers, plus end-to-end CDD automation with ACN-based beneficial owner resolution for companies, SMR and TTR workflows, and a tamper-evident audit trail that exceeds the statutory seven-year minimum.
AML Guard isn’t self-service software you sign up for online. Onboarding starts with a demo, after which your tenant gets configured to your practice’s designated services, risk profile, and workflow, so what you’re using from day one actually matches how your practice operates. If your practice is captured under Tranche 2 and you’d rather build your compliance program on a platform than a folder of templates, book a demo with AML Guard to see how the CDD, reporting, and record-keeping workflows fit your practice.
Sources
- Accounting program starter kit: Getting started | AUSTRAC
- Anti-Money Laundering and Counter-Terrorism Financing Act 2006 (Cth)
- AML/CTF for accountants | CPA Australia
FAQ
Who Must Enrol With AUSTRAC?
Any accounting practice providing a designated service under the Tranche 2 reforms must enrol, with obligations applying from 1 July 2026 for firms captured through the enrolment windows that opened on 31 March 2026.
Does CDD Apply to Clients I Already Had Before My Obligations Started?
Pre-commencement customers have limited exemptions, but CDD can still be triggered if a client’s risk profile changes or they request a new designated service after your obligations began.
Does a Sole Practitioner Still Need a Compliance Officer?
Yes. A sole practitioner must formally appoint a named AML/CTF compliance officer even where that person is themselves; the role can’t simply be left unassigned.
How Quickly Must a Suspicious Matter Be Reported?
Within 24 hours if the suspicion relates to terrorism financing, and within three business days for other suspicious matters, under section 41 of the AML/CTF Act.
How Long Do I Need to Keep AML/CTF Records?
Australian law requires records to be kept for seven years after they stop being relevant to your compliance obligations; some platforms, including AML Guard, retain records for eight years as a margin above that legal minimum.
Recommended
- Tranche 2 AML Australia: your compliance obligations explained
- Tranche 2 customer due diligence in Australia
- AML/CTF Program Documents for Tranche 2
- Acceptable ID documents for Tranche 2 firms
See How AML Guard Works
Tranche 2 obligations are now in force.
Book a 20-minute demo to see how AML Guard supports your compliance from the moment your designated service begins.