Treat an SMSF as a trust customer: establish the fund’s identity, its trustees (and, for a corporate trustee, the trustee’s own beneficial owners), its members as beneficiaries, and anyone else with control. ATO tools such as Super Fund Lookup confirm the fund’s status, never the identity of the people behind it. Enhanced due diligence applies where section 32 of the Act requires it, and records are kept for the periods the Act sets.
TL;DR:
- Verifying an SMSF requires identifying the fund, trustees, beneficiaries, and anyone with control, including reviewing deed clauses and ASIC registry data where applicable.
- The SMSF verification service is used by the fund paying a rollover into an SMSF; it confirms the fund’s details with the ATO, not who the trustees are.
- Enhanced due diligence applies where the fund’s risk is high or another section 32 trigger applies; large unexplained inflows are a reason to look harder, and each decision should be documented.
- Records of verification, deed analysis, screening and officer approvals are kept for the periods the Act sets: CDD records until seven years after the business relationship ends.
- Automated lookups support mechanical checks, but officer judgment is essential for deed review and determining beneficial ownership.
Table of Contents
- What treating an SMSF as a trust customer requires in practice
- What the ATO’s SVS and Super Fund Lookup verify, and their limits
- Initial, enhanced and ongoing CDD under the AML/CTF Rules 2025, applied to SMSFs
- Step-by-step onboarding checklist and workflow for verifying an SMSF
- Timelines, record keeping and evidential standards for SMSF CDD
- How a structured compliance platform supports SMSF verification
- Common pitfalls, red flags and quick prevention tips
- AML Guard: a practical option for SMSF program artefacts and auditable CDD
- FAQ
- Sources
What treating an SMSF as a trust customer requires in practice
An SMSF is a trust, and under AUSTRAC’s guidance on initial CDD for trusts, that means collecting and verifying several distinct elements, not just a single entity name. Members of an SMSF are its beneficiaries, and we need to establish, on reasonable grounds, who stands behind the fund and who controls it.
In practice, this means identifying:
- The fund itself: its full name, ABN and establishing deed.
- Each trustee and anyone who represents the fund with you; for a corporate trustee, the company itself and its own beneficial owners (in an SMSF, usually the member-directors).
- Beneficiaries, which in an SMSF are the fund’s members.
- Anyone else with control under the deed, such as an appointor or protector, since these roles can carry real influence over fund decisions even without legal ownership.
AUSTRAC’s list of a trust’s beneficial owners covers every individual trustee, the beneficial owners of a corporate trustee, any settlor, appointor, guardian or protector, and anyone else with control. In an SMSF the members are usually also the trustees or the trustee’s directors, so the same people appear as beneficiaries and as controllers. Beneficial ownership looks at ownership (25% or more) and at control. Where an SMSF uses a corporate trustee, that company is resolved on its own ACN through ASIC registry data, and the deed clauses that assign control still need an officer’s reading rather than a registry lookup.
What the ATO’s SVS and Super Fund Lookup verify, and their limits
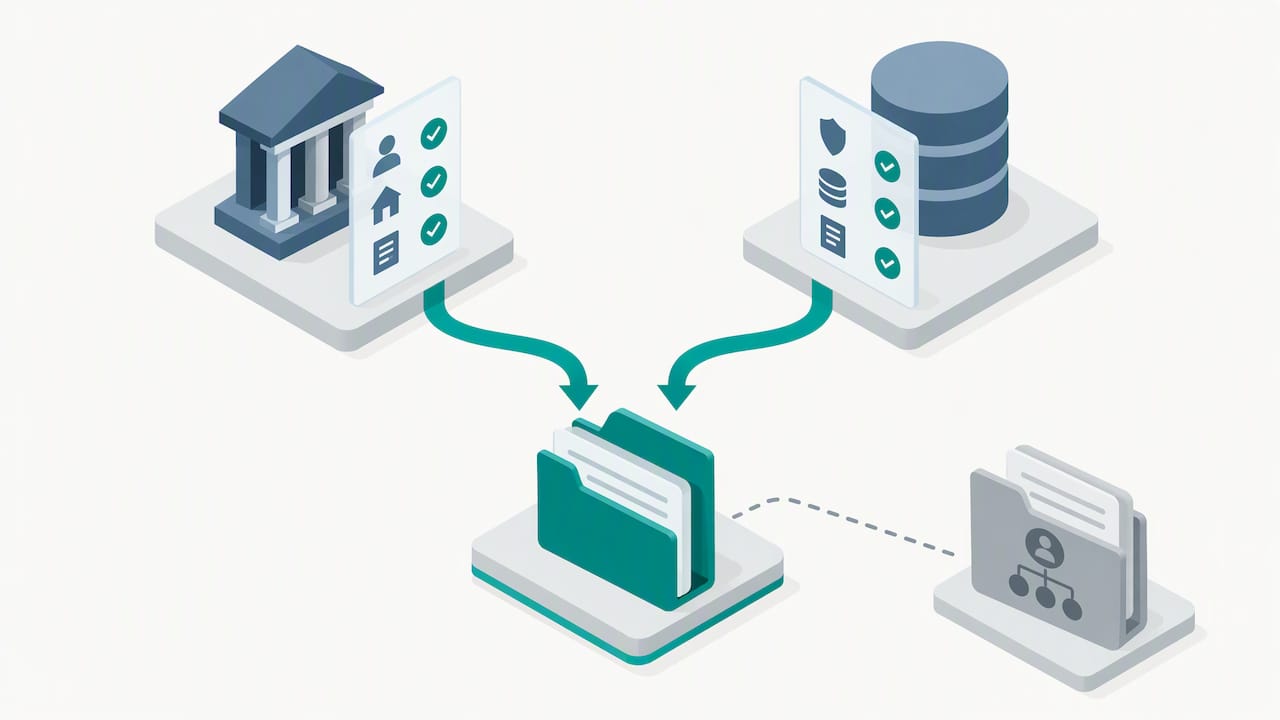
The SMSF verification service (SVS) exists for a specific moment: when a member asks to roll super into an SMSF. The fund paying the rollover, whether APRA-regulated or another SMSF, must use it to check that the receiving fund’s ABN is registered as an SMSF, its complying or regulated status, that the member’s TFN is linked to it, and its bank and electronic service address details. It is not a tool a practitioner runs for AML/CTF purposes, but its outcome shows whether the fund’s details match the ATO’s.
SVS returns one of two outcomes:
- A verified response, confirming the details match.
- A non-verified response, which says whether the mismatch relates to the SMSF or the member, after which the SMSF or member contacts the ATO to correct the details.
Neither SVS nor Super Fund Lookup verifies the identity of a trustee or director. Both confirm the fund’s status and registration; identity verification of the people behind the fund remains a separate obligation under the Act and the Rules.
Initial, enhanced and ongoing CDD under the AML/CTF Rules 2025, applied to SMSFs
The Anti-Money Laundering and Counter-Terrorism Financing Rules 2025 set out how verification, reliance and enhanced measures apply, and for an SMSF these obligations translate into three stages.
- Initial CDD: collect the trust deed and amendments, confirm the fund’s ABN and status, verify each individual trustee, identify a corporate trustee and its beneficial owners, and identify the members as beneficiaries and anyone holding control under the deed. Sources include the deed, ABN Lookup and, for a corporate trustee, ASIC registry extracts.
- Enhanced CDD: applies where the fund’s ML/TF risk is high or another section 32 trigger applies, such as a foreign PEP among the trustees, members or others with control. Indicators worth weighing include unusually large or unexplained inflows, deed clauses that concentrate unusual control in one party, or anything that prompts a suspicious matter assessment. Enhanced measures can include establishing source of funds and source of wealth, obtaining further deed extracts and confirming trustee identity from another source, with the reasons recorded.
- Ongoing CDD: re-verification should be triggered by a change in trustees, an amendment to the deed, or a shift in the fund’s risk profile, not by a fixed calendar alone. Monitoring frequency should match the fund’s assessed risk, and every change that affects beneficial ownership or control needs to be documented at the time it occurs.
Pro Tip: Record the reason for every enhanced CDD decision at the time you make it: anyone reviewing the file months later should be able to see the trigger, the measure applied and who approved it, without needing to ask.
Step-by-step onboarding checklist and workflow for verifying an SMSF
A consistent sequence keeps SMSF onboarding defensible and repeatable.
- Confirm the fund’s identity: check its ABN and status via Super Fund Lookup.
- Request the full trust deed, including any amendments.
- Verify each individual trustee, or where a corporate trustee is used, resolve the company on its ACN through ASIC registry data and verify its beneficial owners (usually the member-directors).
- Determine beneficial owners by ownership and by control, reading deed clauses that name appointors or protectors.
- Identify each member by name as a beneficiary of the fund.
- Screen the fund, each trustee, any corporate trustee and its beneficial owners, the members and anyone else with control against PEP and sanctions lists.
- Document officer approval of the beneficial ownership determination and file all supporting evidence.
Useful evidence includes identity documents or reliable electronic data for each individual, the executed trust deed and its amendments, and ASIC extracts for a corporate trustee. If you cannot establish these matters, you generally cannot start providing the service, and you should consider whether a suspicious matter reporting obligation arises.
The Act and the Rules also allow reliance on another reporting entity’s prior verification in defined circumstances. Where you rely on someone else’s CDD, document the reliance arrangement itself, including what was verified, by whom and when, and assess that arrangement regularly (at least every two years for a CDD arrangement under section 37A) rather than treating it as a one-off.
Timelines, record keeping and evidential standards for SMSF CDD
CDD records are kept until seven years after the business relationship ends (section 111 of the AML/CTF Act), and program records until seven years after they stop being relevant (section 116). AML Guard’s audit trail holds records for 8 years, above the Act’s seven-year minimum.
A defensible SMSF file should hold:
- Identity verification records for each individual: what was checked and the result.
- The relevant deed extracts, including clauses on control or appointment.
- ASIC/ACN lookup results for any corporate trustee.
- Super Fund Lookup or ABN Lookup results for the fund.
- PEP and sanctions screening outputs.
- Officer sign-off on each beneficial ownership determination.
- Any suspicious matter or threshold transaction reports lodged.
A reviewer will look for timestamps on every record, version history where a deed or trustee structure changed, a clear record of who approved each determination, and evidence that is searchable rather than buried in email threads.
How a structured compliance platform supports SMSF verification
A platform built for Tranche 2 obligations earns its keep by keeping the program’s artefacts consistent: the business-wide risk assessment, the AML/CTF policies, the compliance action plan and the staff training manual should all draw from the same underlying answers, since a mismatch between them is hard to defend.
Automation has a clear boundary here. A corporate trustee’s determination runs on its own ACN through ASIC registry data, and that lookup can be automated. Reading the deed and finalising the beneficial ownership determination cannot: those steps require an officer’s judgement, and AML Guard does not trace beneficial owners through a trust directly: it reaches them through the corporate trustee’s own ACN determination.
What automation does well:
- ACN-based lookups for corporate trustees.
- PEP and sanctions screening with ongoing re-screening.
- Tamper-evident storage of every check and approval.
Pro Tip: Use automated lookups to clear the mechanical checks quickly, then spend the time saved on the deed review, which is where the real risk assessment happens.
Common pitfalls, red flags and quick prevention tips
A common mistake is treating Super Fund Lookup or SVS as identity verification; both confirm fund status, neither confirms who a trustee is. A close second is incomplete trustee verification, where a corporate trustee is checked on ASIC but the individuals who own or control it are never identified. Poor deed documentation, where control clauses are never read or filed, leaves a determination with no evidence behind it.
Watch for these red flags:
- A large or unexplained rollover with no clear source of funds.
- Deed clauses granting one party unusually broad appointment or removal powers.
Document every judgement call as you make it, escalate deed questions you can’t resolve internally, and set clear escalation criteria in your AML/CTF policy before you need them.
AML Guard: a practical option for SMSF program artefacts and auditable CDD
Running SMSF verification well means juggling deed review, ASIC lookups, screening and an audit trail that holds up months or years later. AML Guard carries that operational load by producing the business-wide risk assessment, AML/CTF policies, compliance action plan and training manual as one linked set, resolving corporate trustees on their own ACN through ASIC registry data, running PEP and sanctions screening with ongoing re-screening, and retaining every record in an 8-year tamper-evident audit trail, above the Act’s seven-year minimum.
- Officer approval is still required for deed interpretation and every beneficial ownership determination; the platform automates the lookups and the record keeping, not the judgement.
- Firms begin with a demo tailored to their designated services and workflow, or can review plan options on our pricing page.
For a deeper look at how we approach beneficial ownership for trusts and SMSFs more broadly, see our guide on beneficial ownership CDD for trusts, SMSFs and companies.
FAQ
How to do AML verification for an SMSF?
Treat the SMSF as a trust customer: establish the fund’s identity, verify each individual trustee (or a corporate trustee and its beneficial owners), identify the members as beneficiaries and anyone else with control, and screen them all. ATO tools confirm the fund’s status, not the people. Our guide on trust KYC in Australia sets out the broader initial CDD process this sits within.
What are the new AML rules in Australia for SMSFs?
The AML/CTF Act and the Anti-Money Laundering and Counter-Terrorism Financing Rules 2025 govern verification, reliance and enhanced due diligence for all reporting entities, including those onboarding SMSF customers. They require identification of the trust, its trustees, its beneficiaries and its beneficial owners, with enhanced measures where the risk is high or another section 32 trigger applies.
What should be checked when onboarding an SMSF for AML purposes?
Confirm the fund’s ABN and status, obtain the trust deed, verify each trustee individually or resolve a corporate trustee through its ACN, and identify beneficiaries and anyone with control under the deed. Run PEP and sanctions screening and document officer approval of the beneficial ownership determination before proceeding.
How long does AML verification take for an SMSF?
Timing depends on how quickly the trustees provide the deed, identity information and anything extra that enhanced due diligence needs. Registry checks (ABN Lookup, Super Fund Lookup, ASIC) are quick; the deed review and any source of funds questions take longer.
Does the ATO’s Super Fund Lookup verify a trustee’s identity?
No. Super Fund Lookup confirms an SMSF’s ABN and regulatory status only. Trustee identity verification remains a separate step under the Act and the AML/CTF Rules.
Sources
- SMSF verification service for rollovers | ATO
- Anti-Money Laundering and Counter-Terrorism Financing Rules 2025
- Initial CDD for trust | AUSTRAC
- Anti-Money Laundering and Counter-Terrorism Financing Act 2006 (Cth)
Recommended
- Tranche 2 AML Australia: your compliance obligations explained
- Tranche 2 customer due diligence in Australia
- AML risk scoring that stands up to AUSTRAC
- AML/CTF Program Documents for Tranche 2
See How AML Guard Works
Tranche 2 obligations are now in force.
Book a 20-minute demo to see how AML Guard supports your compliance from the moment your designated service begins.