Secure client intake for AML means routing every identity document through one encrypted channel with named requests, role-based access and a tamper-evident audit trail, never through email. Combined with minimal retention of passport and licence images and a seven-year AML/CTF record-keeping schedule, this satisfies Tranche 2 customer due diligence while keeping the reporting entity’s Privacy Act exposure low. Magic-link and supervised tablet modes cover the two most common client interactions without adding IT overhead.
TL;DR:
- Moving all identity documents through a single encrypted channel with role-based access and audit logs prevents email-related security breaches.
- Implementing named document requests and automated retention rules ensures correct files are collected, securely stored, and properly deleted when no longer needed.
- Using portal modes like magic links or supervised tablets reduces admin workload and strengthens verification during client onboarding.
- Pushing only status flags to the CRM while keeping sensitive evidence within a secure portal maintains privacy without sacrificing auditability.
- Fixing common intake flaws, such as replacing email and vague requests, can be achieved quickly with minimal cost and effort by adopting targeted controls.
Table of Contents
- What Tranche 2 requires of your client intake process
- Secure intake checklist: controls to stop email, limit data, and create audit-ready records
- Intake portal operating modes and practical patterns that reduce admin work
- Record keeping versus privacy: reconciling seven-year AML retention with the Privacy Act
- Where firms fall short: common failures and quick, low-cost fixes
- How to choose and configure a secure intake solution or process
- Author perspective: how AML Guard implements the checklist in practice
- How AML Guard helps implement secure client intake
- Sources
- FAQ
What Tranche 2 requires of your client intake process
Tranche 2 brings real estate agencies, buyers agents, property developers, conveyancers, law firms, accounting practices, and trust and company service providers into the AML/CTF regime as reporting entities. Any of these businesses providing a designated service, such as arranging a property sale, settling a conveyance, or forming a trust, must now run customer due diligence at the point of intake, not after the fact.
The obligation starts with a documented AML/CTF program. AUSTRAC’s guidance on the reforms sets out the requirement for a business-wide risk assessment and matching policies, and a supervisor reviewing your file will expect the risk assessment, the policies, the compliance action plan and the staff training records to tell the same story. A training manual that describes procedures your policies do not mention is a red flag, not a formality.
Client due diligence itself splits along a predictable path once intake begins:
- Identity verification for individuals: name, date of birth, and residential address checked against a reliable and independent source.
- Beneficial ownership resolution for companies, trusts and SMSFs, typically anchored to the entity’s ACN. AUSTRAC’s guidance on ownership and control structures describes the layered checks expected when a trust or SMSF sits behind a corporate trustee.
- Risk assessment of the client and the transaction, informed by the intake data collected.
- Approval by a compliance officer before the matter proceeds.
- Record creation, so the decision and its reasoning survive an audit years later.
Once onboarding is approved, the work does not stop. Ongoing monitoring means re-screening clients against sanctions and adverse media lists on a cadence set by their risk rating, and watching for the triggers that require a suspicious matter report under section 41 or a threshold transaction report. Intake is where most of this evidence originates, which is exactly why weak intake security creates weak compliance evidence.
Secure intake checklist: controls to stop email, limit data, and create audit-ready records
Email is the single worst channel for collecting identity documents. It has no access control once sent, no expiry, and it scatters copies of passports and driver’s licences across inboxes, sent folders and phone backups that nobody is tracking. The principle is simple: replace scattered email and shared drives with one encrypted upload channel, and the rest of the intake process becomes far easier to secure.
Build your intake process around these controls:
- One encrypted channel only. TLS in transit and AES-256 at rest, with no fallback to email for “urgent” cases.
- Named document requests. Ask for “certified copy of driver’s licence, front and back” rather than “your ID”, so clients upload the right file the first time.
- Retention rules mapped to each item. Decide at request stage what gets kept and for how long, not after the file arrives.
- Role-based access control. Only the staff working a matter can view its documents; approval gates CDD before it proceeds.
- Tamper-evident audit logs. Every upload, view, download and approval carries a timestamp and an approver note.
- Expiring, revocable links. A magic link that dies after use or after a set window closes off the biggest risk of a forgotten open request.
- Minimal image retention. Where a verification token or short-lived proof of check will do, keep that instead of the original passport scan.
These controls work together: encryption both ways, RBAC, tamper-evident trails and magic-link access patterns, because each control addresses a different failure mode. Encryption stops interception. RBAC stops internal snooping. The audit log is what proves, months later, that the right person approved the right file at the right time.
Pro Tip: Give every uploaded document a legal-purpose tag the moment it lands (identity verification, beneficial ownership evidence, risk assessment support). That single habit is what makes automated retention and fast audit exports possible later.
A client-pays option, where the transaction party funds their own identity check through a secure payment link, also removes a friction point that otherwise tempts staff to accept a document by whatever channel is fastest.
Intake portal operating modes and practical patterns that reduce admin work
Not every client interaction looks the same, and a secure intake process needs more than one mode to match how people actually onboard.
- Remote magic-link mode. No client account or login required. The client receives a single secure link that opens a form and an upload area, ideal for off-site onboarding when a buyer or vendor is interstate or simply prefers to do this from home.
- Supervised tablet or in-person mode. Staff capture documents and run verification during an appointment, settlement or signing, with biometric liveness checks completed on the spot rather than chased up afterwards.
- High-volume, multi-party flows. Property transactions and trust structures often involve several roles at once, buyer, seller, trustee, director. Templated named requests for each role, paired with status-only flags pushed to a CRM, keep multi-party matters from collapsing into a pile of loose emails.
Biometric liveness and ACN-based lookups earn their place when the client’s risk rating or the transaction type calls for stronger verification, and both should sit behind an approval gate: a compliance officer signs off before the matter moves to the next stage, not before.
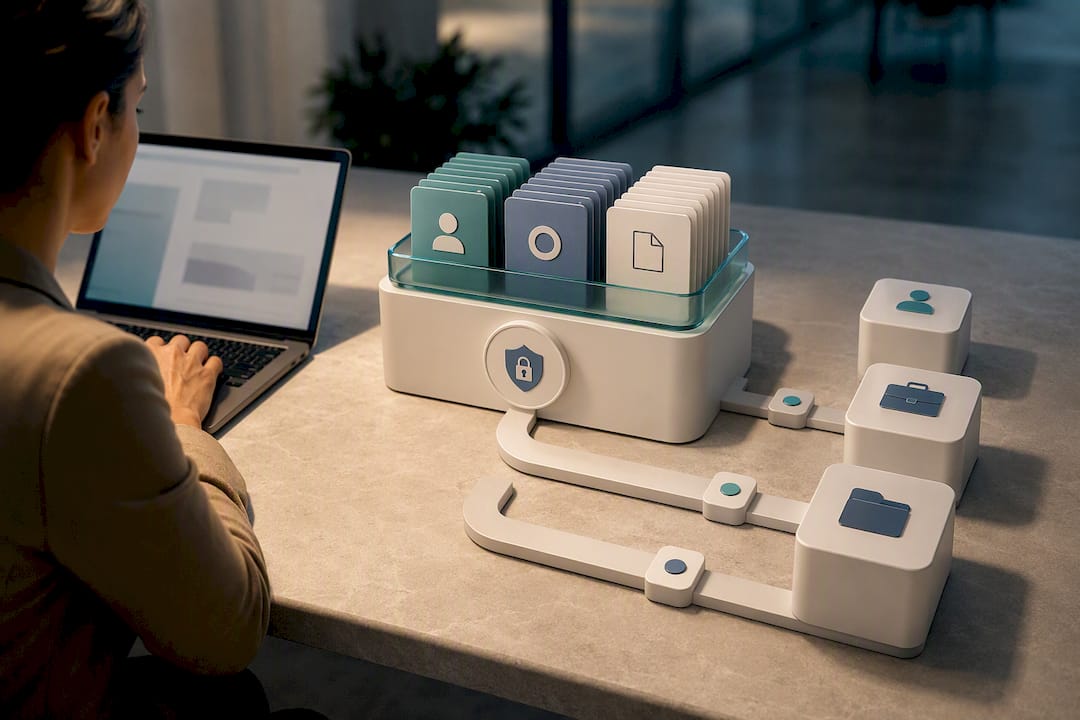
On integration, the rule is simple. Push compliance status to your practice management or CRM system, approved, pending, or flagged, but keep the underlying identity documents and CDD evidence inside the one system built to secure them. A practical description of portal-based onboarding under Tranche 2 makes the same case: a single source of truth for audit exports beats CDD data duplicated across three different systems that each need their own security review.
Record keeping versus privacy: reconciling seven-year AML retention with the Privacy Act
AML/CTF record-keeping and the Privacy Act pull in opposite directions, and treating them as one rule is where firms get into trouble. AML/CTF obligations require you to keep evidence of the CDD you performed, the risk assessment you reached, and the reporting you filed, for seven years. The Privacy Act, by contrast, expects you to minimise how much personal information you hold and for how long, which means the seven-year clock applies to your compliance records, not to every scanned copy of a passport that ever crossed your desk.
The fix is tagging documents by legal purpose the moment they arrive, so retention automation can enforce different timelines on different files:
- Keep seven years: the CDD outcome, risk assessment notes, approval records, SMR and threshold transaction report evidence.
- Delete once verification is complete: the original passport or licence image itself, where the legal basis for holding it no longer applies and a verification token or certified summary satisfies the audit requirement.
- Review case by case: supporting documents whose retention need depends on the client’s risk rating or an open regulatory matter.
Seven-year retention exists to protect audit evidence, not to justify an indefinite personal document archive. A firm that keeps every ID scan forever because “AML requires seven years” has misread the obligation, and created a much larger Privacy Act liability in the process.
Where firms fall short: common failures and quick, low-cost fixes
Most intake failures are not exotic. They are the same three or four habits repeating across hundreds of files, and each one has a fix that does not require a procurement cycle.
- Stop email this week. Deploy one magic-link upload channel and update every intake template to point clients there instead of an inbox.
- Replace vague requests with named ones. “Send your ID” becomes “certified copy of driver’s licence, front and back, JPG or PDF”, cutting the back-and-forth that eats staff time.
- Add an approval gate. Require a timestamped approver note before CDD proceeds to the next stage, so every file has a named decision attached to it.
- Set retention rules and run one cleanup. Automate deletion for non-required files and schedule a single pass to clear out anything sitting past its purpose.
- Measure what changed. Track reminders sent per client, time to complete a full request list, and time spent reconstructing evidence for an audit. These are the clearest signs a fix has worked.
Pro Tip: Run the fix on one matter type first, say, standard residential settlements, before rolling it out across every service line. A single successful pilot gives you a template you can copy rather than a redesign you have to defend.
How to choose and configure a secure intake solution or process
Whether you build this internally or adopt a dedicated platform, the same evaluation criteria apply. Treat these as non-negotiable:
- Encryption in transit and at rest. TLS for anything moving, AES-256 for anything stored.
- Role-based access control, so exposure is limited to the staff actually working a file.
- Tamper-evident audit logs covering uploads, views, downloads and approvals, not just logins.
- Configurable retention, so different document types can expire on different schedules.
- Expiring, revocable links, closing off forgotten or leaked access.
- ACN-based beneficial-ownership lookups, matching what AUSTRAC’s ownership guidance expects for company, trust and SMSF structures.
- Exportable audit packages, so producing evidence for a supervisor takes minutes rather than a week of file reconstruction.
Once the platform is chosen, configuration matters as much as the tool itself. Build named-request templates for each service line, set the approval gate so no CDD step proceeds without a signed-off decision, and confirm staff training records are captured alongside the policy documents they relate to, not filed separately. A Tranche 2 CDD walkthrough is worth reviewing here if your matters regularly involve non-individual clients or layered ownership structures. Set a re-screening cadence tied to each client’s risk rating, and confirm your risk scoring produces reasoning a supervisor can actually follow, not just a number.
On integration, push status flags only, approved, pending, flagged, into your CRM or practice management system. Raw identity documents and CDD evidence stay inside the one system built to secure and audit them, never duplicated into general record systems that were never designed for sensitive personal information.
Author perspective: how AML Guard implements the checklist in practice
Most firms treat identity document security and AML program documentation as one problem. They are not. A risk assessment can be sound and a training manual can be current, yet the passport image collected last week can still be sitting in someone’s inbox. AML Guard’s intake portal exists because that gap is where the real exposure lives: documents never travel by email, and every access to them becomes part of the same audit trail that also records the CDD decision. Linked artefacts, risk assessment, policies, training, matter, because a supervisor checks for consistency across all four; a portal that generates them from one set of answers removes the mismatch a downloaded template cannot avoid. Start with one intake flow, measure it, then expand.
How AML Guard helps implement secure client intake
A dedicated encrypted intake portal replaces email inboxes and shared drives, so identity documents never travel by an unsecured channel. Named document requests, expiring magic links, role-based access control and a tamper-evident audit trail come configured to designated services, and beneficial ownership resolution runs directly against a company’s ACN.
A demo shows an example configured intake flow, the approval gate in action, and an audit export a supervisor could review, plus the option to let transaction parties pay for their own verification, credited back against subscription costs. Compliance status flows to an existing CRM as a status flag only, so teams keep working the tools they already know. Book a demo through AML Guard to see a configured intake flow built around your services.
Sources
FAQ
What Makes Client Intake “secure” Under AML/CTF Rules?
Secure intake means identity documents move through one encrypted channel with role-based access and a tamper-evident audit trail, never as email attachments, with retention bounded by legal purpose rather than convenience.
Why Is Email the Biggest Risk in AML Client Onboarding?
Email attachments have no access control, no expiry and no audit trail once sent, scattering copies of passports and licences across inboxes and devices that nobody is actively securing.
How Long Must AML/CTF Records Be Kept?
Customer due diligence outcomes, risk assessments and reporting evidence must be retained for seven years, but that obligation covers compliance records, not an indefinite copy of every identity document collected.
Does AML Guard Push Client Documents Into My CRM?
No. AML Guard pushes only compliance status flags, such as approved or pending, into a connected CRM like REX, while identity documents and CDD evidence stay inside its own audit-controlled portal.
What Is the Fastest Low-cost Fix for Weak Intake Security?
Replace email with one encrypted magic-link upload channel this week, switch to named document requests, and add a timestamped approval gate before any CDD step proceeds.
Recommended
- The Client Intake Portal: How Smart Agencies Onboard Clients for AML
- Tranche 2 AML/CTF Guide for Australian Real Estate Agents | 1 July 2026
- Tranche 2 AML Australia: your compliance obligations explained
- AML risk assessment template for Tranche 2 firms
See How AML Guard Works
Tranche 2 obligations are now in force.
Book a 20-minute demo to see how AML Guard supports your compliance from the moment your designated service begins.