Australian reporting entities need AML/CTF training records that show who was trained, on which module, when, and with what result, alongside personnel due diligence records for the same people. Under section 116, records demonstrating compliance with Part 1A of the AML/CTF Act must be retained for 7 years after they stop being relevant.
TL;DR:
- Training records should be linked to specific module versions and include details on delivery method, assessment results that show understanding, and a sign-off.
- Training and personnel due diligence records are kept until 7 years after they stop being relevant (section 116), with the reasoning for the start date recorded.
- Generating training, policies and the risk assessment from the same answers makes it easier to keep the three consistent.
- An attendance sheet on its own shows little; AUSTRAC suggests recording how you assessed understanding and the results.
- Regular backups, timestamped entries, restricted access, and role-based mapping improve data integrity, especially as staff numbers and content updates increase.
Table of Contents
- What records reporting entities must keep under the AML/CTF Act
- What a defensible training record must show
- Organising, storing and retaining training records
- Linking training records to personnel due diligence and role risk
- A practical checklist and template for training records
- How a compliance platform can produce audit-ready training records
- Where audits actually go wrong
- Turning training records into an audit-ready system
- Sources
- FAQ
What records reporting entities must keep under the AML/CTF Act
Section 116 of the Anti-Money Laundering and Counter-Terrorism Financing Act 2006 (Cth) requires a reporting entity to keep records that are reasonably necessary to demonstrate compliance with its Part 1A program obligations. AUSTRAC’s record-keeping overview groups these into several practical categories, each serving a different purpose when a supervisor or internal auditor comes looking.
The business-wide ML/TF risk assessment and the AML/CTF policies sit at the top: they establish what the entity decided its risks were and how it chose to manage them. Customer due diligence files sit underneath, showing identity verification, screening outcomes and ongoing monitoring for each customer. Transaction records capture the activity itself, and records of any threshold transaction or suspicious matter reports sit beside them. Personnel due diligence and training records complete the set, evidencing that the people running the program were suitable for their roles and equipped to apply it.
Each category answers a different audit question:
- The risk assessment and policies show the entity understood its exposure and built a proportionate response.
- CDD files show individual customers were verified and screened before or during service delivery.
- Transaction and reporting records show the entity acted on what it observed.
- Personnel due diligence and training records show the people applying the program were vetted and capable.
These categories are connected rather than separate filing exercises. A risk assessment that flags a high-risk service line means little if the personnel handling that service line cannot show training tailored to it, and a training register means little if it cannot be tied back to the roles the risk assessment identified as sensitive. The AML/CTF Rules 2025 set out the training and personnel due diligence requirements (sections 5-8 and 5-9) that these records are meant to prove were followed. Reporting entities building or refreshing their program documents can see how the risk assessment, policies and training manual are meant to work as one linked set in our guide to AML/CTF program documents for Tranche 2.
What a defensible training record must show
A training record that survives scrutiny is not a sign-in sheet. AUSTRAC’s AML/CTF training guidance gives examples of what to record: who completed the training, what was delivered (topics, format, content and content version), how understanding was assessed and the results, and each person’s training history. That goes well beyond a name and a date.
At minimum, a defensible record should capture:
- The staff member’s name and role, so the record can be matched to a position with defined AML/CTF responsibilities.
- The module name and its version or content identifier, so the entity can show exactly what was taught at that point in time.
- The delivery method, whether e-learning, an in-person session or a hybrid format.
- The date the training was completed.
- The assessment type used and the result achieved, not merely attendance.
- The name of the person who approved or signed off the completion, and the date of that approval.
- The next refresher trigger and the reasoning behind it, whether that is a calendar date, a role change or a material update to the program.
Linking each entry to the specific content version matters more than it might seem. If the training manual is updated after a regulatory change, a record that simply says “AML training completed” gives no way to tell whether the staff member learned the old approach or the new one. Tying the record to a version number or content identifier closes that gap.
AUSTRAC also expects you to monitor whether training works, for example through post-training assessment of understanding. A signed attendance sheet on its own does not show whether the person understood the material or could apply it to their role; an assessment result tied to a specific module version, and a sign-off, do.
Pro Tip: Treat every training record as evidence you might need to produce on short notice, not as a filing exercise you complete and forget.
Organising, storing and retaining training records
The retention rule is not complicated, but it is easy to get wrong in practice. Part 1A records, which include training and personnel due diligence records, must be kept for 7 years after they stop being relevant under section 116 of the Act. The harder question is deciding when a record stops being relevant. For an ongoing staff member, one reasonable point is the end of their engagement with the entity. For training tied to a specific matter or project, it may be the closure of that matter. AUSTRAC’s record-keeping overview leaves this judgement to the entity, so documenting the reasoning behind a chosen retention start date is itself part of a defensible file.
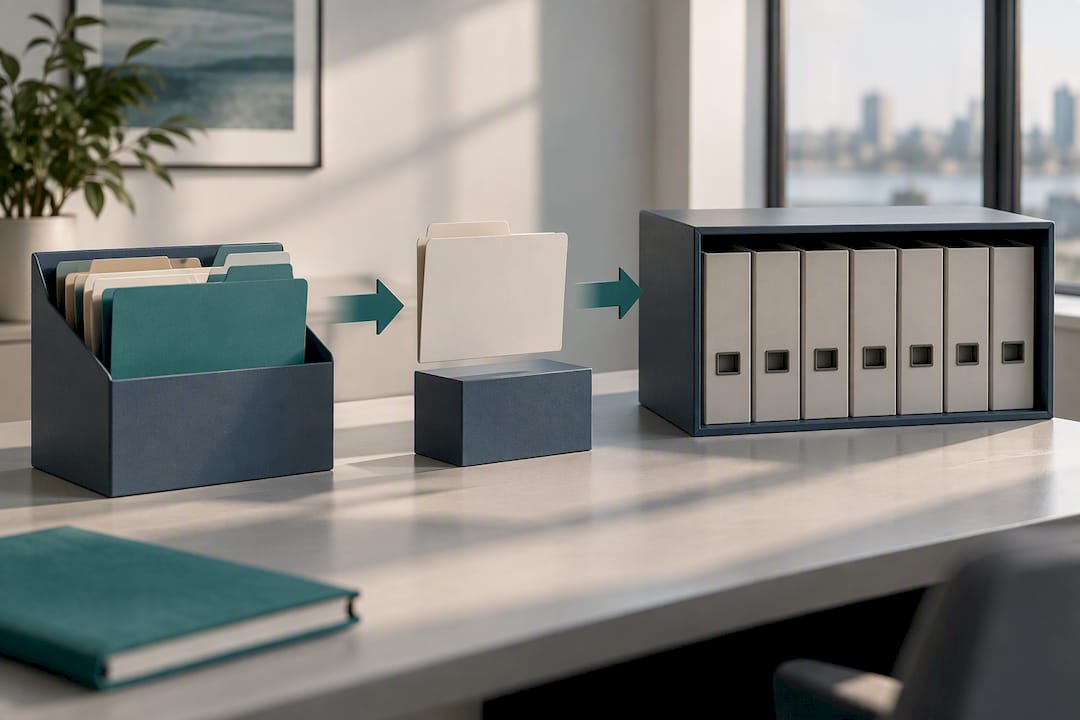
7 years after a record stops being relevant is the period section 116 of the Act sets for Part 1A records, and it applies to training and personnel due diligence files as much as to the risk assessment and policies. CDD and transaction records run on their own clocks (sections 111 and 107).
On the technical side, a defensible register typically relies on:
- Timestamped entries that cannot be silently altered after the fact.
- Version control on training content, so a record can always be matched to the exact module a staff member sat.
- Regular backups held separately from the live system.
- Access controls that restrict who can edit completed records, as distinct from who can view them.
Operationally, someone needs to own the register, chase overdue training, and flag missed sessions for escalation before they become a gap an auditor finds first. Linking the training calendar to HR onboarding and offboarding dates helps close the loop, since a departing staff member’s training file is exactly the kind of record that needs a clear “ceased to be relevant” date recorded against it.
Linking training records to personnel due diligence and role risk
Training and personnel due diligence are not separate obligations sitting side by side. AML/CTF policies must deal with training for people whose functions are relevant to the Act and with due diligence on those same people, as set out in section 26F(4)(d) and (e). AUSTRAC’s guidance covers personnel due diligence and training together, starting from the roles that need both, so a training record without a matching personnel due diligence file tells only half the story.
A workable mapping documents, for each relevant role:
- The role description and why it was identified as relevant to the Act.
- The specific modules assigned to that role, given its risk exposure.
- The assessment standard applied and the result achieved.
- The approval trail confirming who signed off both the training and the personnel due diligence check.
A staff member handling high-risk customer onboarding, for instance, would sit against a more rigorous assessment standard and a shorter refresher cycle than someone in a support role with no direct customer contact, and the mapping should make that difference visible rather than leaving it implied.
A practical checklist and template for training records
A short checklist keeps a training register consistent across staff and locations:
- Confirm the role has been assessed as relevant to the Act before assigning training.
- Record the module name, version and delivery method for every completion.
- Capture the assessment result, not just attendance.
- Record an approver’s name and sign-off date for every entry.
- Set and document the next refresher trigger and the reasoning behind it.
- Store the record with a timestamp that cannot be altered after entry.
A simple register can use these column headings: staff name, role, module name and version, delivery method, completion date, assessment result, approver, refresher trigger, and retention start date. Each column should hold an actual value rather than a placeholder; an empty assessment result column is itself a gap worth closing before an auditor asks about it.
For guidance on what the training content itself should cover, see our AML training manual guide, which sets out module structure separately from the record-keeping obligations covered here.
- Checklist items above follow the examples in AUSTRAC’s training guidance, plus the sign-off and refresher fields we recommend.
- Storage practices should match the access control and backup points already covered.
How a compliance platform can produce audit-ready training records
Some firms build this register manually in a spreadsheet; others use a platform. AML Guard, for example, runs multilingual training modules and keeps completion records in its 8-year tamper-evident audit trail, above the Act’s seven-year minimum.
Consistency between the risk assessment, the policies and the training manual is easy for a reviewer to test, and that consistency is easier to maintain when the three documents come from the same underlying data.
Because the training manual, policies and risk assessment are generated from the same set of answers, the manual stays consistent with the policies, and each completion record sits in the same audit trail. That reduces the manual reconciliation work involved in proving who completed which training, and when.
Where audits actually go wrong
A common weakness is not missing training. It is training that cannot be tied to a role’s risk level, or evidence that shows attendance without showing understanding. Prioritise records that are timestamped, version-matched and instantly retrievable. Where evidence is thin, fix the weakest role-risk pairings first, not the easiest ones.
Turning training records into an audit-ready system
Building and maintaining this register by hand is achievable for a small team, but it becomes harder to sustain as staff numbers grow, roles change, and training content gets updated to reflect new guidance. AML Guard produces the training manual, AML/CTF policies and the business-wide risk assessment as one linked set, so the manual matches the policies and risk assessment it was built from.
AML Guard runs multilingual training modules with completion records held in its 8-year tamper-evident audit trail, so a compliance officer responding to an AUSTRAC request can find a staff member’s training history without searching through separate files. Features relevant to record keeping include:
- Linked program artefacts, so the training manual matches the policies and risk assessment it was built from.
- Multilingual training with tracked completion records.
- An 8-year tamper-evident audit trail, above the Act’s seven-year minimum.
If your current register relies on spreadsheets and sign-in sheets, book a demo to see how the platform handles training records, or check pricing for the plan that suits your team.
Sources
- Record keeping overview | AUSTRAC
- Anti-Money Laundering and Counter-Terrorism Financing Act 2006 (Cth)
- Anti-Money Laundering and Counter-Terrorism Financing Rules 2025
- AML/CTF training | AUSTRAC
FAQ
How long do I retain AML/CTF training records?
Training records are Part 1A records, and under section 116 they must be kept for 7 years after they stop being relevant. AUSTRAC leaves that point to your judgement; for an ongoing staff member, the end of their engagement is one reasonable choice.
What are the current AML/CTF rules in Australia?
The governing framework is the Anti-Money Laundering and Counter-Terrorism Financing Act 2006 (Cth) together with the AML/CTF Rules 2025, which set out program, personnel due diligence and training obligations for reporting entities. Tranche 2 obligations for real estate, legal, accounting, and trust and company service providers are now in force.
Is there free online AML/CTF training available in Australia?
AUSTRAC provides e-learning modules as educational material, but these are supplementary and do not replace training tailored to a reporting entity’s own risks and roles. A reporting entity still needs its own program-specific training and a record showing staff completed it.
How often must AML/CTF training be refreshed?
There is no fixed refresher interval in the Act or the Rules. The Rules require initial training and ongoing training appropriate to each person’s function and the risks relevant to it, and AUSTRAC says the frequency depends on those functions and risks. Record why you chose the interval.
What does AML Guard record for staff training?
AML Guard runs multilingual training modules and stores completion records in its 8-year tamper-evident audit trail, above the Act’s seven-year minimum.
Recommended
- Tranche 2 AML Australia: your compliance obligations explained
- AML risk assessment template for Tranche 2 firms
- AML/CTF policy template for Tranche 2 firms
- AML training real estate: what agencies must do
See How AML Guard Works
Tranche 2 obligations are now in force.
Book a 20-minute demo to see how AML Guard supports your compliance from the moment your designated service begins.